A security analyst receives a notice about a possible data breach. The report identifies unapproved, current access dates for files found in the following personnel archives:
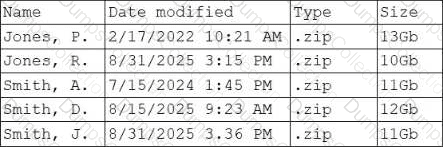
Which of the following actions should the analyst take first?
An analyst prepares an after action report following an incident in which multiple systems were compromised over several days.
The analyst provides raw event logs from each compromised system in the report and determines that a patient-zero system cannot be found.
Which of the following should the analyst do to determine the patient-zero system?
A security operations center analyst is using the command line to display specific traffic.
The analyst uses the following command:
$tshark -r file.pcap -Y "http or udp"
Which of the following will the command line display?
Which of the following actions should an incident response analyst take during the recovery phase of the incident response process?
A vulnerability scanner shows discrepancies between the number of Internet Protocol (IP) addresses across the sites being scanned and the number of systems reporting into the patching system.
Which of the following actions will resolve this issue?
A new security operations center (SOC) manager joins a team that struggles to meet service-level agreements (SLAs). The alert backlog continues to increase daily.
Which of the following will the manager most likely need to do?
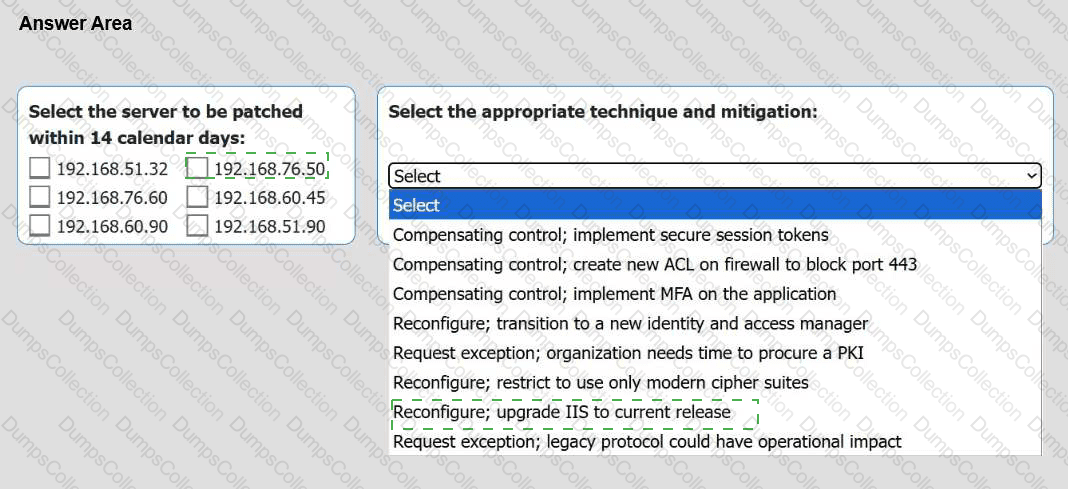
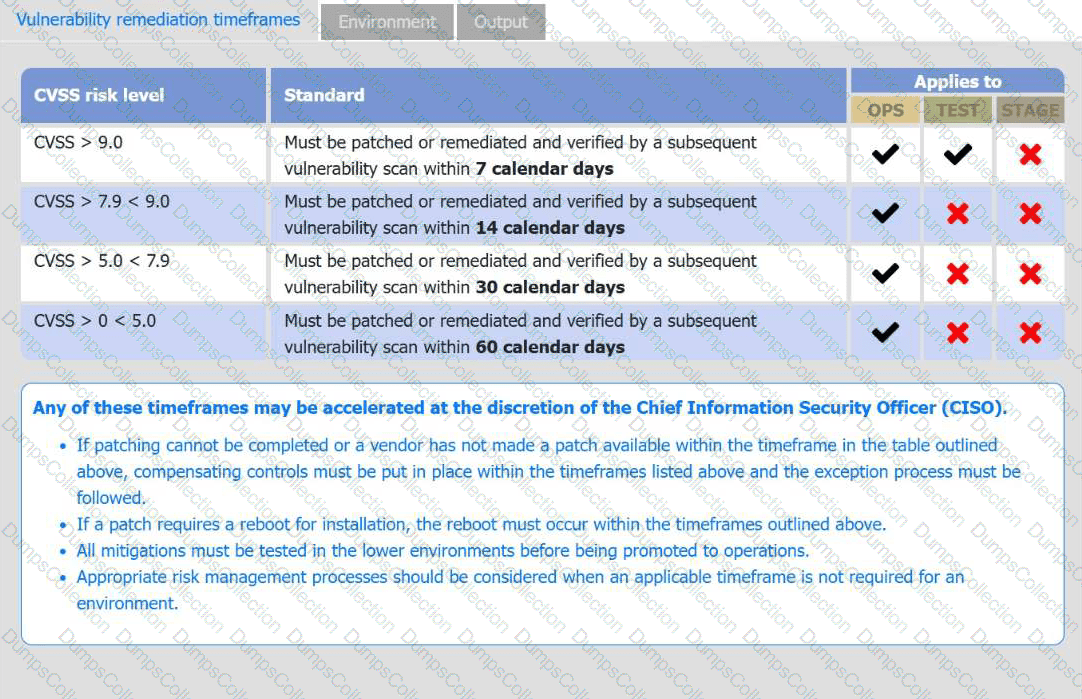
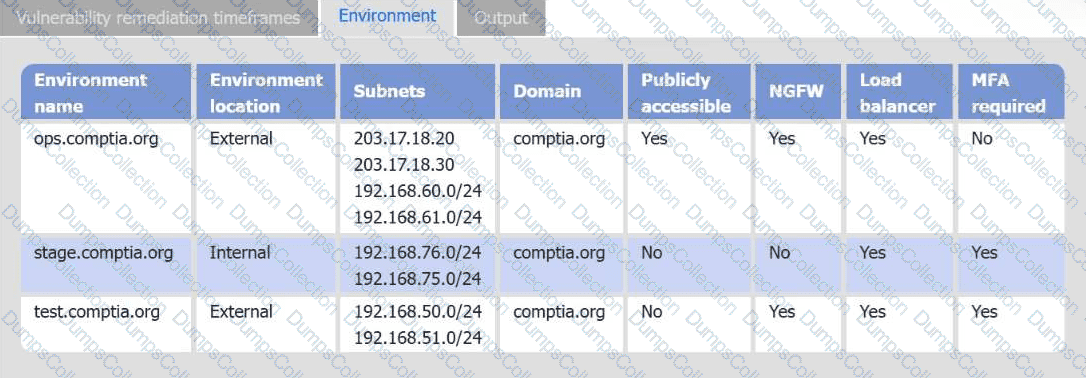
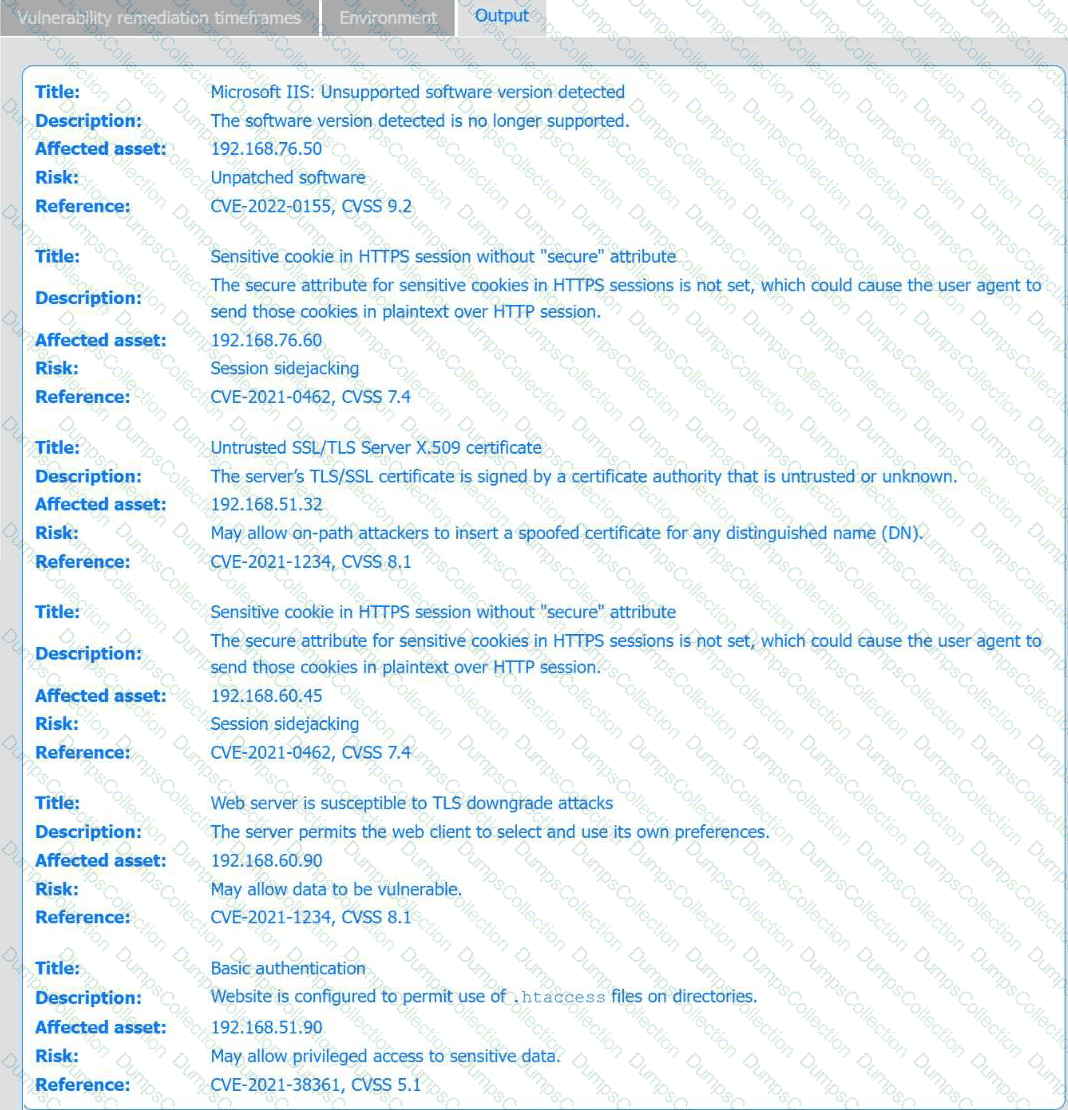
A systems administrator is reviewing the output of a vulnerability scan.
INSTRUCTIONS -
Review the information in each tab.
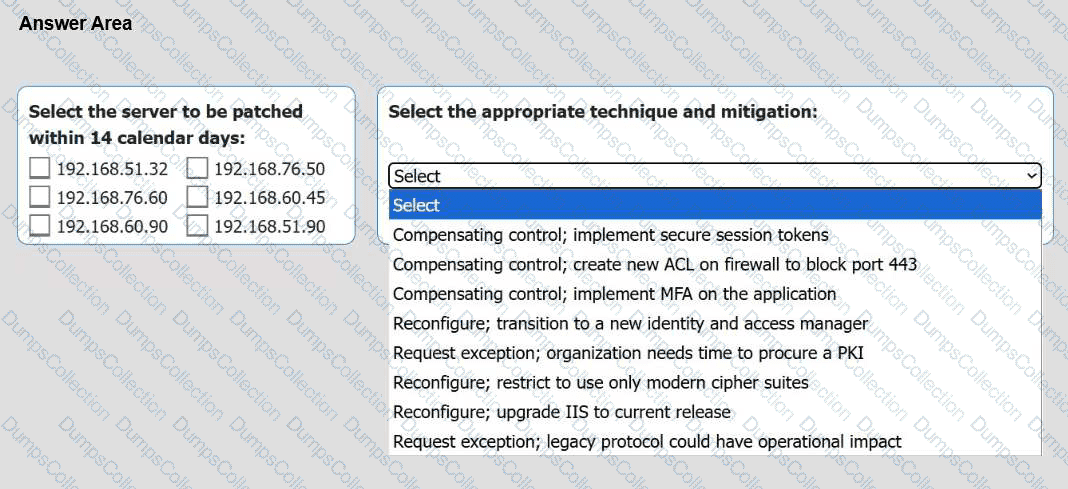
Based on the organization’s environment architecture and remediation standards, select the server to be patched within 14 days and select the appropriate technique and mitigation.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
A binary file that might contain malicious code is hosted on an isolated machine. An analyst wants to quickly detect the malicious code.
Which of the following should the analyst use?
A security analyst analyzes the output of a web application access log for a company based in the United States.
Given the following output:
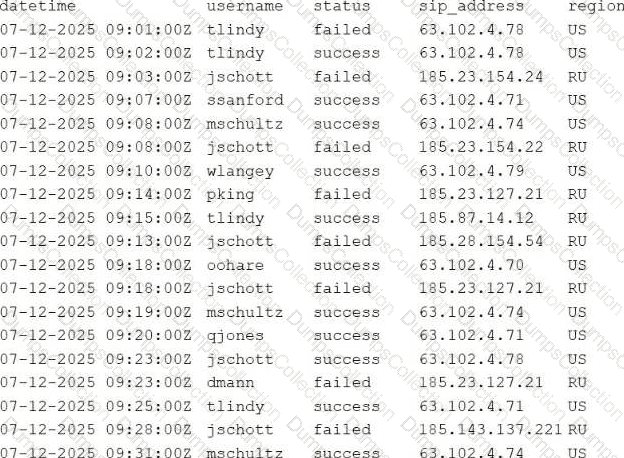
Which of the following users should be investigated first?
Which of the following is the most important reason why tactics, techniques, and procedures (TTP) are beneficial to a defensive strategy?
TESTED 26 Sep 2026