Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: discbf75DC

Page: 1 / 5
Total 47 questions
Exam Code: CY0-001                Update: Oct 29, 2026
Exam Name: CompTIA SecAI+ v1 Exam

CompTIA CompTIA SecAI+ v1 Exam CY0-001 Exam Dumps: Updated Questions & Answers (October 2026)

Question # 1

A security architect performs threat modeling of an AI system. The architect needs to determine which attacks can be performed against the system.

Which of the following actions should the architect take next?

A.

Leverage a large language model (LLM) to map likely attack paths based on the code base.

B.

Quantify the risk of known vulnerabilities identified in the AI system.

C.

Identify trust boundaries and perform threat modeling with Open Worldwide Application Security Project (OWASP) Top 10.

D.

Analyze MITRE Adversarial Threat Landscape for AI Systems (ATLAS) for tactics, techniques, and procedures (TTPs).

Question # 2

Which of the following would most likely be used to prove that an image is AI generated?

A.

Human validation

B.

Guardrails

C.

Diffusion

D.

Watermarking

Question # 3

A group of security engineers is developing a SIEM system that will be able to ingest data from multiple structured and unstructured sources, have a chatbot integrated with an LLM that the security analyst can interact with, and provide insights from the SIEM alert data.

Which of the following techniques should the security engineers consider before collecting the data from the respective sources?

A.

Balancing

B.

Verification

C.

Cleansing

D.

Vector storage

Question # 4

User experience is declining since the launch of a large language model (LLM) in internal networks.

Which of the following should be the highest priority for the prompt engineers?

A.

Customer success management

B.

Sales life cycle

C.

Quality control

D.

Business objectives

Question # 5

A developer is proposing a new AI application for human resources systems. Which of the following are the most important considerations?

A.

Geniality and appeal

B.

Privacy and security

C.

Graphics and design

D.

Brevity and summarization

Question # 6

An organization is concerned with the exposure of sensitive data.

Which of the following is the most relevant security concern?

A.

Overfitting

B.

Model inversion

C.

Data normalization

D.

Hyperparameter tuning

Question # 7

A security analyst who is reviewing logs notices the following:

• Suspicious inputs are present and contain character look-alikes.

• Strange character substitutions

• Odd spacing

• Inputs that appear to be broken sentence structures

Which of the following best explains what the user was utilizing?

A.

Disinformation

B.

Obfuscation

C.

Misinformation

D.

Anonymization

Question # 8

A security analyst is aware of an active penetration test in the environment. The analyst examines SIEM log data and notices the following AI system output:
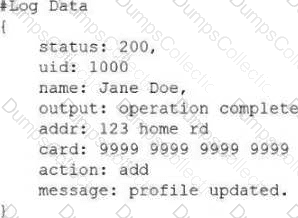
Which of the following is the vulnerability that has occurred and the control the analyst should implement?

A.

The vulnerability is prompt injection, and the analyst should use endpoint detection response (EDR).

B.

The vulnerability is model hallucinations, and the analyst should develop output validations.

C.

The vulnerability is jailbreaking, and the analyst should utilize role-based access control.

D.

The vulnerability is sensitive information disclosure, and the analyst should employ masking.

E.

The vulnerability is role impersonation, and the analyst should use validation.

Question # 9

During an update, an AI system flags some potential compatibility issues and provides recommendations. An administrator reviews the recommendations before addressing the issues.

Which of the following processes describes this scenario?

A.

Data validation

B.

Data preparation

C.

Human-in-the-loop

D.

Model evaluation

Question # 10

Security analysts want to track potential user behavior anomalies over time. Which of the following is the most comprehensive approach?
A.

Using an AI-enabled scanner to compare user permissions to other users in the department

B.

Using an agentic large language model (LLM) to search for multiple instances of a username in logs

C.

Leveraging browser plug-ins that monitor for uncommon sites visited by a user

D.

Running automated playbooks that monitor standard deviations from a user baseline

Page: 1 / 5
Total 47 questions

Most Popular Certification Exams

Payment


Contact us

Site Secure

mcafee secure

TESTED 30 Oct 2026