You are asked to configure a query to run every 15 minutes, automatically searching for specific registry modifications across all endpoints. Which FortiEDR feature must you configure? (Choose one answer)
A collector triggers a suspicious security incident that is initially flagged as potentially malicious. The environment is connected to the FortiEDR Cloud Service (FCS) for classification. How does FCS process the event for accurate classification? (Choose one answer)
Which two statements correctly describe the IoT probing process on FortiEDR? (Choose two answers)
Refer to Exhibit.
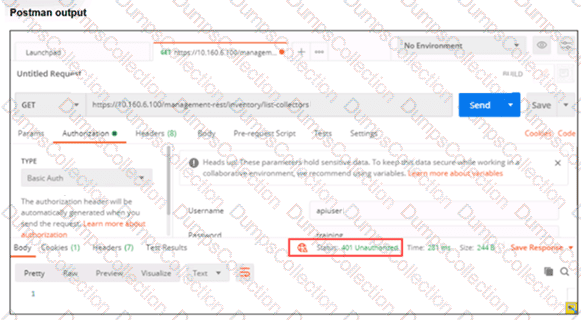
Based on the Postman output shown in the exhibit, why is the user receiving an unauthorized error? (Choose one answer)
Refer to the exhibit:
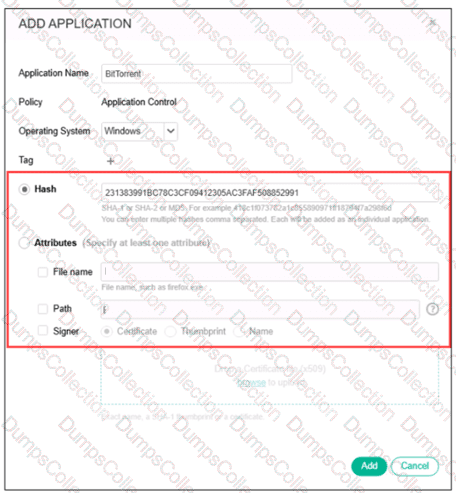
You are asked to block applications based on hash attributes. Which two factors must you consider when applying the hash value? (Choose two answers)
What action does an on-premises reputation server take when it receives a hash request that is not found in its local database? (Choose one answer)
Refer to the exhibits.
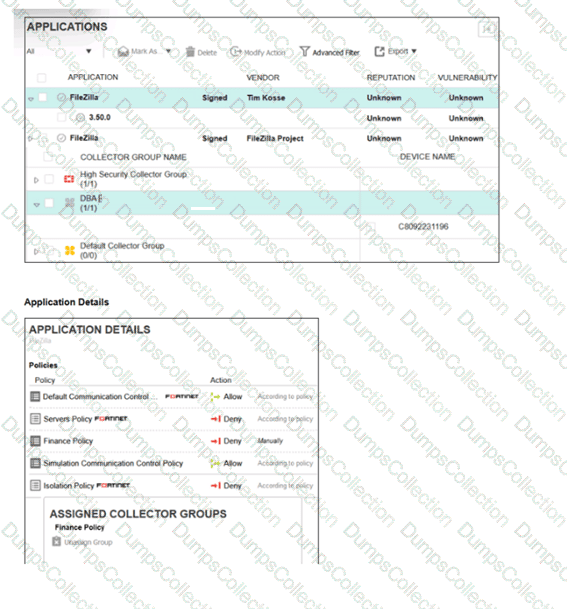
The application policy logs and application details are shown. Collector C8092231196 is a member of the Finance group. In this scenario, what must you do to block the FileZilla application? (Choose one answer)
Refer to the exhibit.
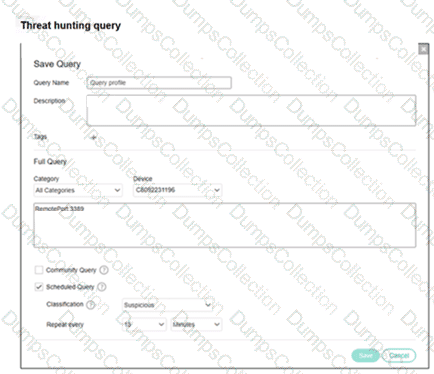
Based on the exhibit, which statement about this threat hunting query is true? (Choose one answer)
Which two criteria are required for integrating FortiEDR with the Fortinet Security Fabric? (Choose two answers)
Refer to the Exhibit:
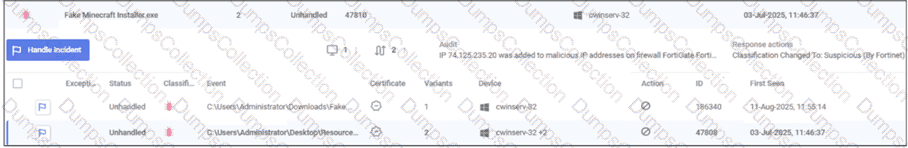
Based on the incident details shown in the exhibit, which two statements about this incident are true? (Choose two answers)
TESTED 02 Nov 2026