Pre-Winter Special Sale - 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: best70

Page: 1 / 2
Total 14 questions
Exam Code: NSE6_FSM_AN-7.4                Update: Sep 19, 2026
Exam Name: Fortinet NSE 6 - FortiSIEM 7.4 Analyst

Fortinet Fortinet NSE 6 - FortiSIEM 7.4 Analyst NSE6_FSM_AN-7.4 Exam Dumps: Updated Questions & Answers (September 2026)

Question # 1

Refer to the exhibit.
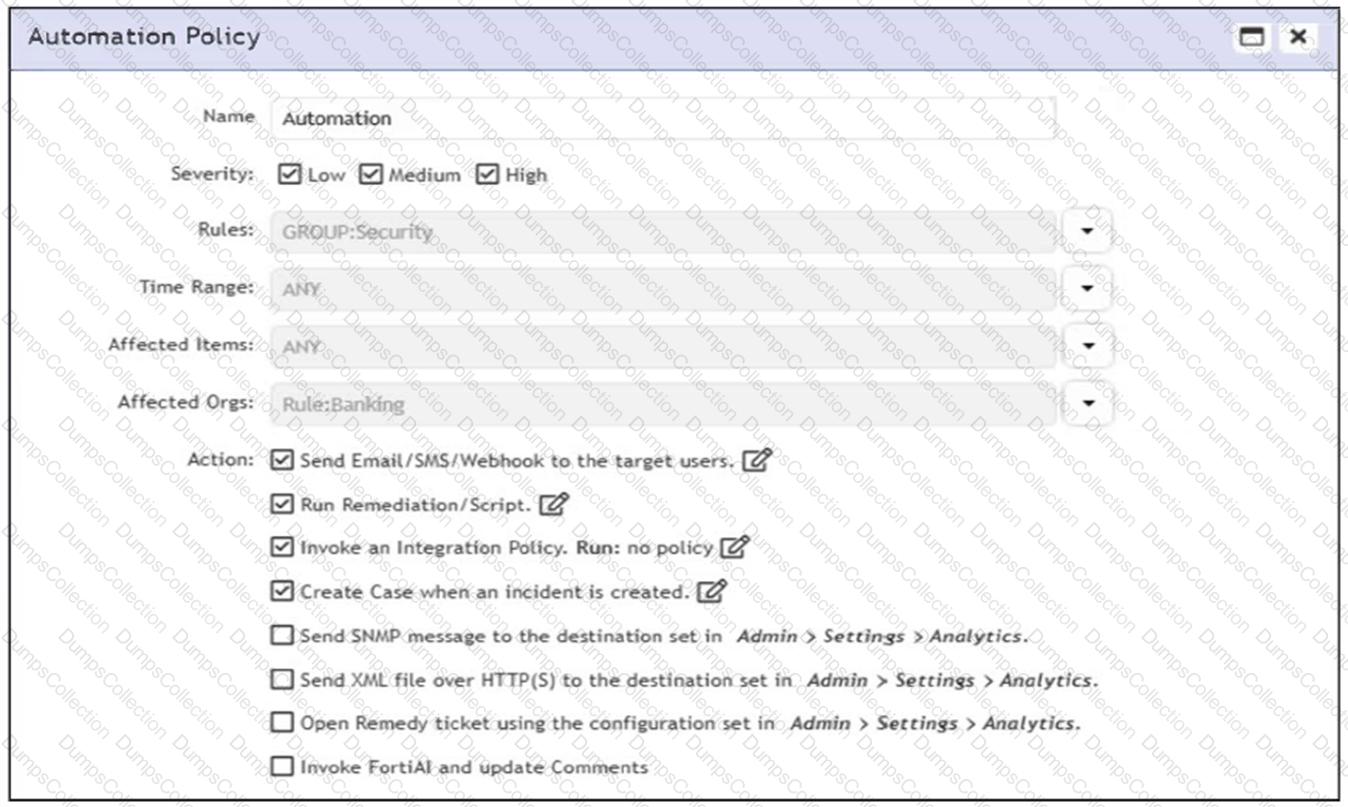
According to the automation policy configuration shown in the exhibit, what happens if an associated rule triggers?

A.

FortiSIEM runs the remediation script, because that takes precedence over all other options.

B.

FortiSIEM performs all selected actions.

C.

FortiSIEM fails to the integration policy, because no policy is defined.

D.

FortiSIEM sends an email, because that is first on the list.

Question # 2

When configuring anomaly detection machine learning, in which step must you select the fields to analyze?

A.

Design

B.

Schedule

C.

Prepare Data

D.

Train

Question # 3

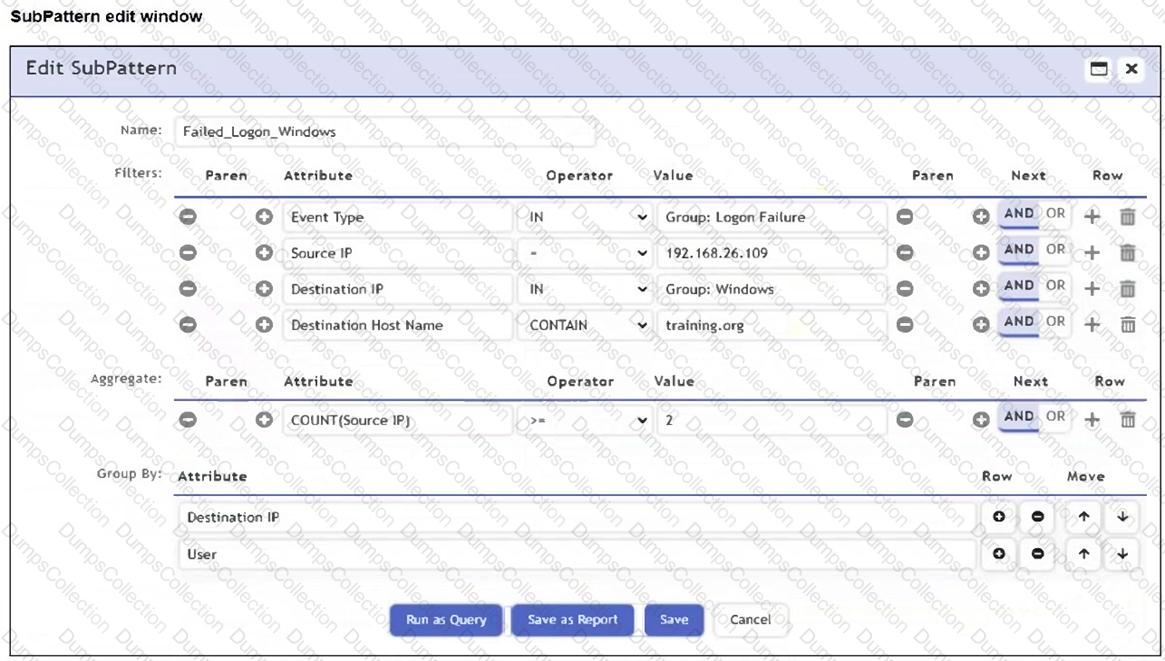
Refer to the exhibit.

An analyst is troubleshooting the rule shown in the exhibit. It is not generating any incidents, but the filter parameters are generating events on the Analytics tab.

What is wrong with the rule conditions?

A.

The Event Type refers to a CMDB lookup and should be an Event lookup.

B.

The Destination Host Name value is not fully qualified.

C.

The Group By attributes restricts which events are counted.

D.

The Aggregate attribute is too restrictive.

Question # 4

Which analytics search can be used to apply a user and entity behavior analytics (UEBA) tag to an event for a failed login by the user JSmith?

A.

User = smith

B.

Username NOT END WITH jsmith

C.

User IS jsmith

D.

Username CONTAIN smit

Question # 5

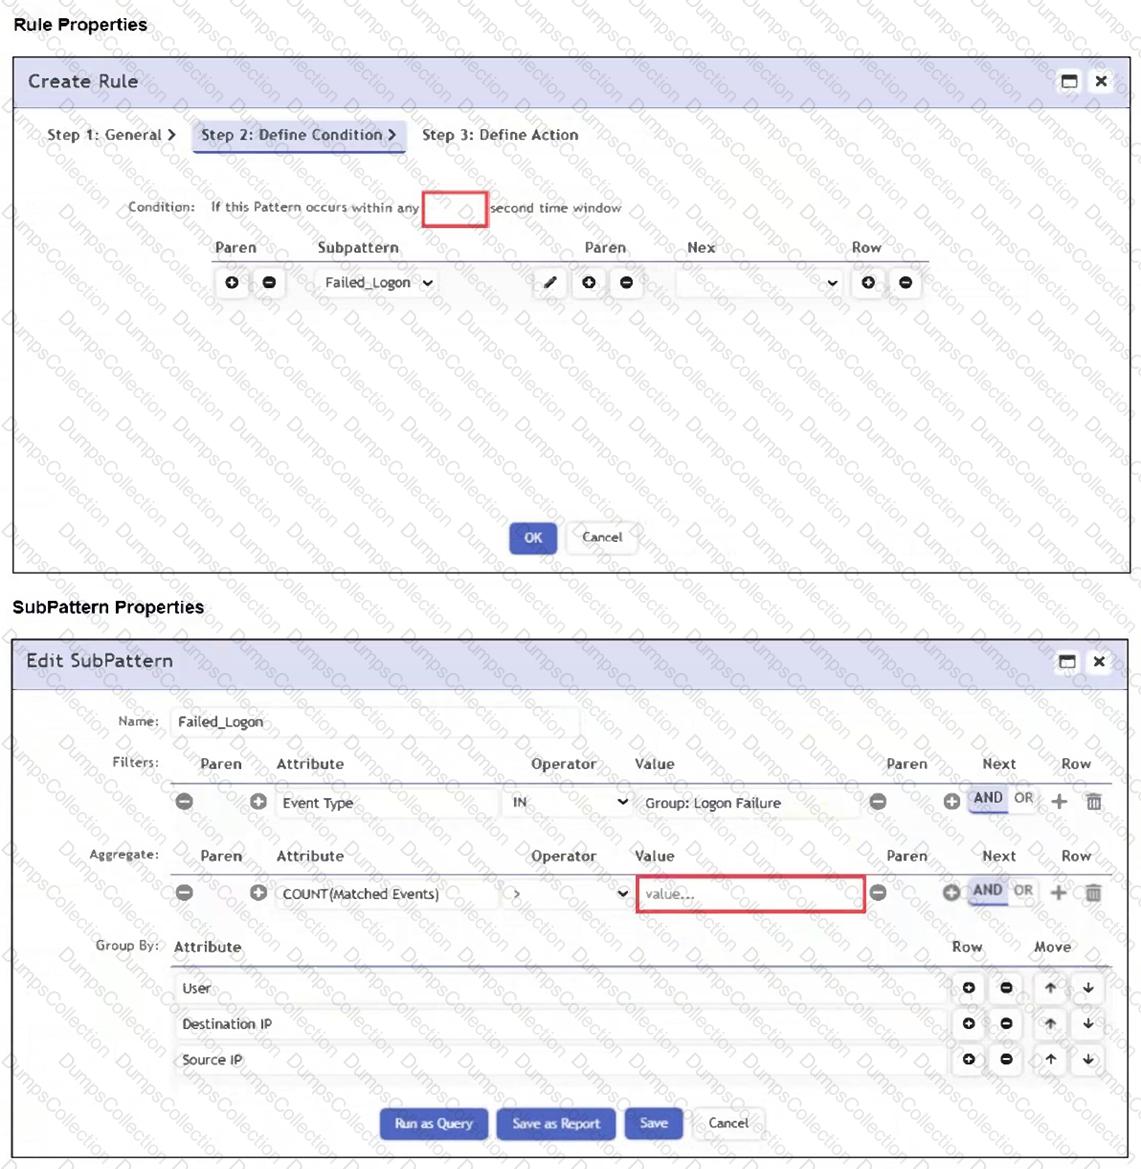
Refer to the exhibit.

An analyst wants the rule shown in the exhibit to trigger when three failed login attempts occur within three minutes.

What should the values be for the condition time window and aggregate count?

A.

Time window 180 seconds, aggregate count 3

B.

Time window 180 seconds, aggregate count 2

C.

Time window 90 seconds, aggregate count 3

D.

Time window 90 seconds, aggregate count 2

Question # 6

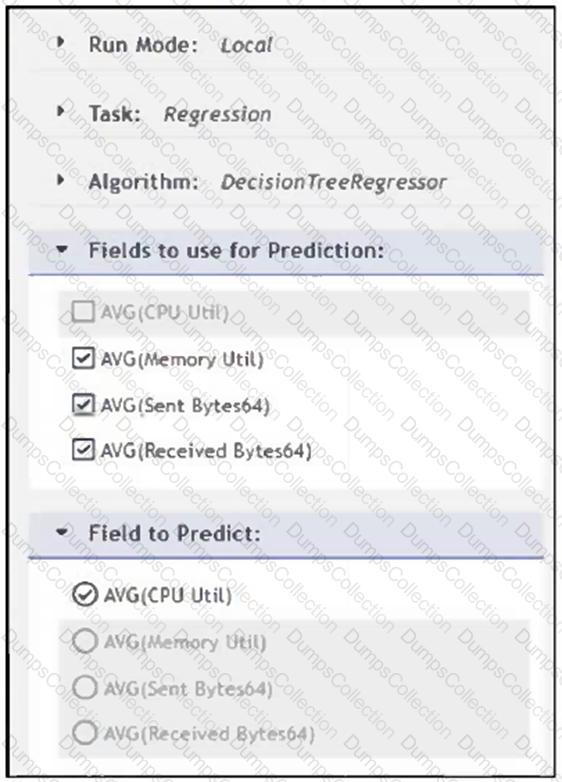
Refer to the exhibit.

What will happen when a device being analyzed by the machine learning configuration shown in the exhibit has consistently high memory utilization?

A.

FortiSIEM will update the regression tables for memory utilization, and average sent and received bytes.

B.

FortiSIEM will trigger an incident for high memory utilization.

C.

FortiSIEM will lower the CPU utilization trigger requirement for CPU utilization.

D.

FortiSIEM will update the model with a higher memory utilization average value.

Question # 7

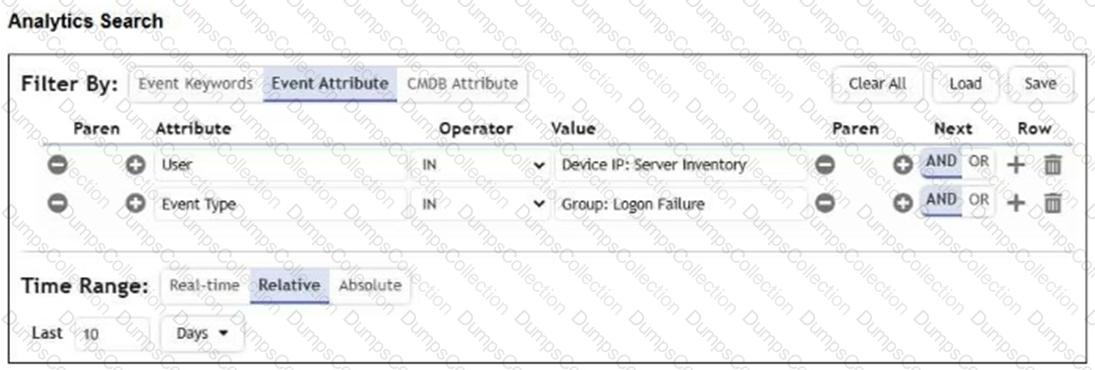
Refer to the exhibit.

The analyst is troubleshooting the analytics query shown in the exhibit.

Why is this search not producing any results?

A.

The Time Range is set incorrectly.

B.

The inner and outer nested query attribute types do not match.

C.

You cannot reference User and Event Type attributes in the same search.

D.

The Boolean operator is wrong between the attributes.

Question # 8

Refer to the exhibit.

An analyst is trying to generate an incident with a title that includes the Source IP, Destination IP, User, and Destination Host Name. They are unable to add Destination Host Name as an incident attribute.

What must be changed to allow the analyst to select Destination Host Name as an attribute?

A.

The Destination Host Name must be selected as a Triggered Attribute.

B.

The Destination Host Name must be set as an aggregate item in a subpattern.

C.

The Destination Host Name must be added as an Event Type in FortiSIEM.

D.

The Destination IP event attribute must be removed.

Question # 9

Refer to the exhibit.

As shown in the exhibit, why are some of the fields highlighted in red?

A.

Unique values cannot be grouped

B.

The attribute COUNT(Matched Events) is an invalid expression.

C.

No RAW Event Log attribute information is available.

D.

The Event Receive Time attribute is not available for logs.

Question # 10

What are two required components of a rule? (Choose two.)
A.

Exception policy

B.

Subpattern

C.

Detection Technology

D.

Clear policy

Page: 1 / 2
Total 14 questions

Most Popular Certification Exams

Payment


Contact us

Site Secure

mcafee secure

TESTED 19 Sep 2026