Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: discbf75DC

Page: 1 / 2
Total 16 questions
Exam Code: NSEI_OTS_AR-7.6                Update: Oct 17, 2026
Exam Name: Fortinet NSE I - OT Security 7.6 Architect

Fortinet Fortinet NSE I - OT Security 7.6 Architect NSEI_OTS_AR-7.6 Exam Dumps: Updated Questions & Answers (October 2026)

Question # 1

Refer to the exhibit.
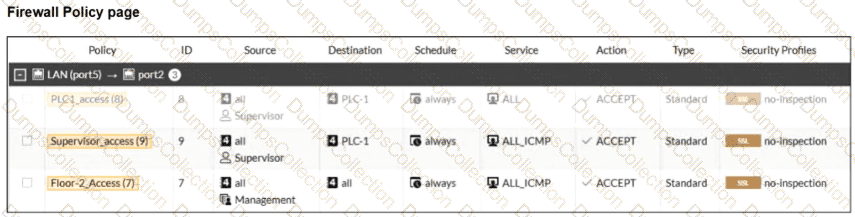
A firewall policy page is shown. To improve the security of your OT network, you have configured a Supervisor profile in the firewall policies, as shown in the exhibit. However, a supervisor is reporting that he cannot ping PLC-1. What are the two reasons? (Choose two answers)

A.

The supervisor must first authenticate using a protocol such as HTTPS or Telnet.

B.

The Supervisor profile is not configured in the remote server.

C.

The firewall policy ID 8 is not enabled.

D.

The CLI parameter auth-on-demand is set to always.

Question # 2

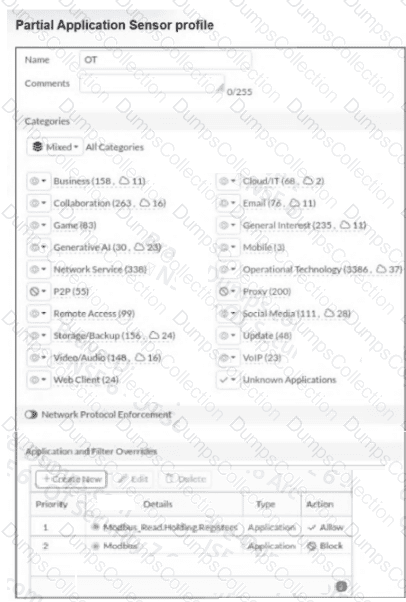
Refer to the exhibit.

A partial Application Sensor profile is shown. When you apply this profile in firewall policy, which two statements are correct? (Choose two answers)

A.

OT signatures are enabled.

B.

All OT protocols are monitored.

C.

Modbus write commands are blocked.

D.

A log is provided for each Modbus read holding registers command.

Question # 3

Which characteristic do the following industrial protocols share: Ethernet/IP, EtherCAT, and POWERLINK?

A.

They provide real-time data transmission.

B.

They follow the complete OSI model.

C.

They use a client-server architecture for communication.

D.

They provide a combination of ring and star topologies.

Question # 4

According to the IEC 62443 standard, your security level is 4 . What is your OT environment defending against? (Choose one answer)

A.

Intentional cyberthreats posed by skilled malicious users

B.

An intentional attack with low resources

C.

A syndicate of cyber extortion with extensive resources

D.

A casual exposure

Question # 5

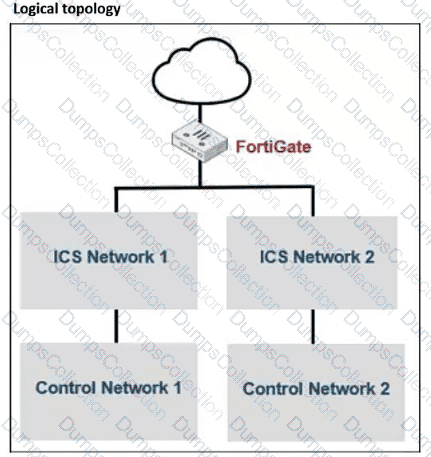
Refer to the exhibit.

A partial OT network is shown.

The OT network is divided into two main networks with a FortiGate device operating in NAT mode.

How can you further segment network 1 from network 2?

A.

You can configure universal ZTNA.

B.

You can configure the FortiGate interface as an implicit software switch.

C.

You can configure two traffic VDOMs.

D.

You can configure different forward domain IDs for network 1 and network 2.

Question # 6

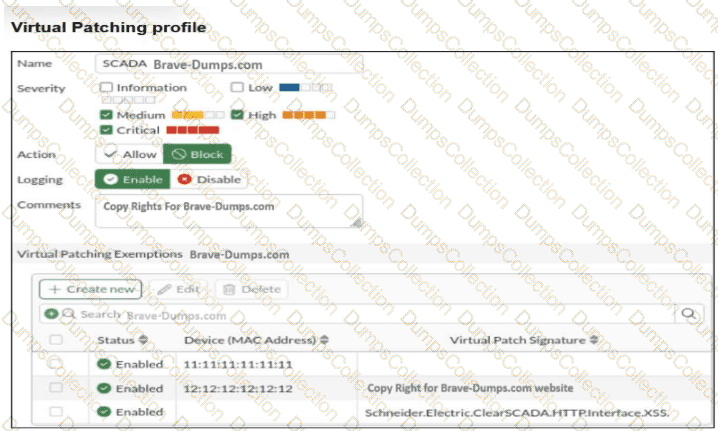
Refer to the exhibit.

A Virtual Patching profile is shown. You have recently updated your SCADA system and would like to apply the SCADA virtual patching profile. Which two statements about this profile are correct? (Choose two answers)

A.

Only the vulnerability Schneider.Electric.ClearSCADA.HTTP.Interface.XSS is still present.

B.

Low severity signatures are not blocked for the device with the MAC address 12:12:12:12:12.

C.

This profile blocks critical severity signatures for all the devices.

D.

The device with the MAC address 11:11:11:11:11 is considered to have no vulnerabilities.

Question # 7

Which industrial protocol does not support VLANs? (Choose one answer)

A.

[Not clearly visible in the exhibit]

B.

Ethernet over industrial protocol

C.

EtherCAT

D.

Modbus over TCP

Question # 8

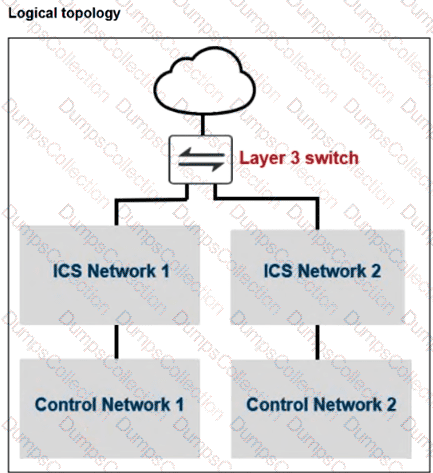
Refer to the exhibit.

A partial OT network is shown. You must improve the security of this OT network and implement internal segmentation between network 1 and network 2. How can you achieve the segmentation? (Choose one answer)

A.

You can configure universal ZTNA.

B.

You can configure one traffic VDOM.

C.

You can configure an explicit software switch.

D.

You can configure forward domain IDs for each network.

Question # 9

Refer to the exhibit.

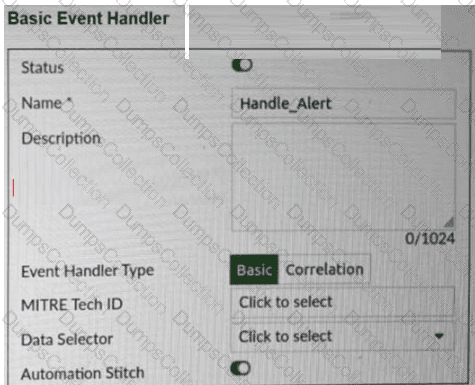
A basic event handler is shown. You have enabled Automation Stitch to automate the handling of an alert. Which two steps must you take to use this automation stitch? (Choose two answers)

A.

You must configure Action on FortiAnalyzer.

B.

You must configure a Playbook task on FortiAnalyzer.

C.

You must configure a FortiAnalyzer event handler trigger on FortiGate.

D.

You must configure Rules on FortiAnalyzer.

Question # 10

Refer to the exhibit.

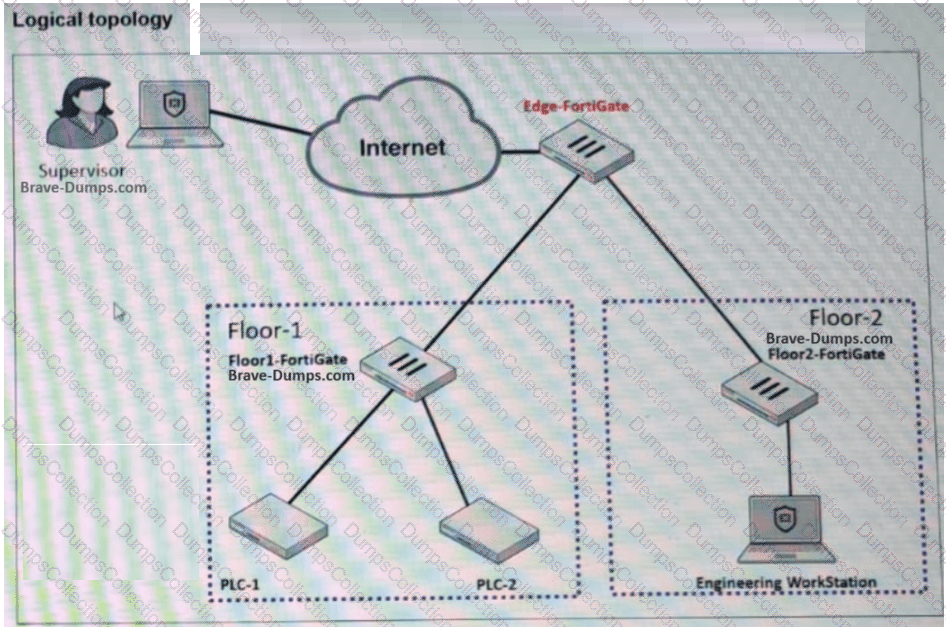
A partial OT network is shown. You want to provide the supervisor with secure remote access. Which two features can you implement on Edge-FortiGate ? (Choose two answers)
A.

IPsec

B.

FortiToken

C.

SD-WAN

D.

FSSO

Page: 1 / 2
Total 16 questions

Most Popular Certification Exams

Payment


Contact us

Site Secure

mcafee secure

TESTED 17 Oct 2026