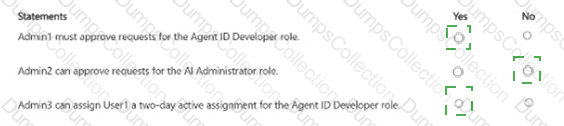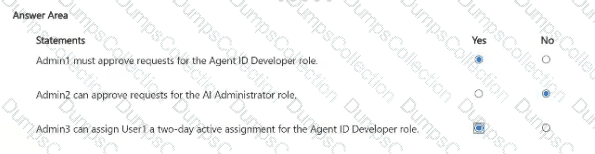
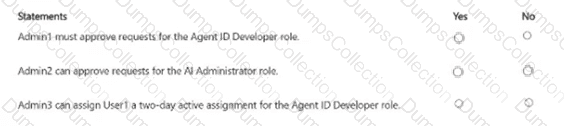
For each of the following statements, select Yes if the statement is true Otherwise, select No.
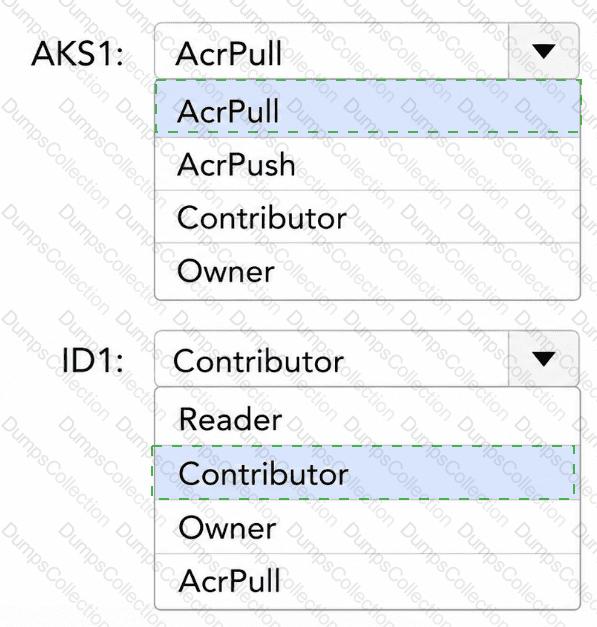
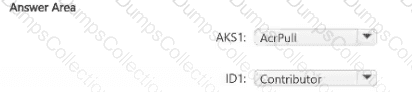
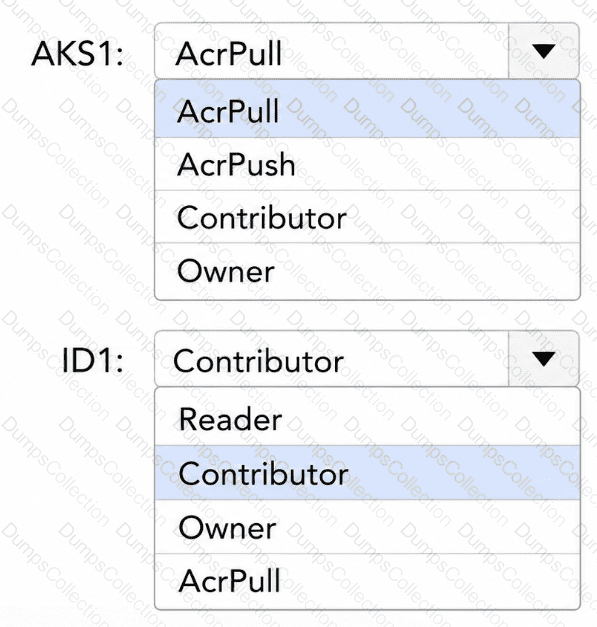
You need to configure the AKS1 and ID 1 managed identities to meet the technical requirements. The solution must follow the principle of least privilege.
Which role should you assign to each identity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to implement the planned change for SQLdb1
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point
You have an Azure subscription that has the Microsoft Defender for Cloud Foundational Cloud Security Posture Management (CSPM) plan enabled.
You have an Amazon Web Services (AWS) account connected to Defender for Cloud for posture management.
In Defender for Cloud, security recommendations for the resources in Azure and AWS have a risk level of Not evaluated.
You need to ensure that Defender for Cloud assigns a risk level to the recommendations.
What should you do?
You have an Azure subscription.
You need to deploy an Azure virtual WAN to meet the following requirements:
•Create three secured virtual hubs located in the East US. West US, and North Europe Azure regions.
•Ensure that security rules sync between the regions.
What should you use?
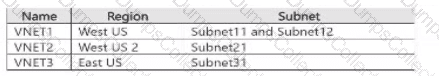
The subscription contains the virtual machines shown in the following table.
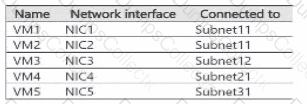
On Nl1I, you configure an application security group named ASG1.
On which other network interfaces can you configure ASG1?
You have an Azure Functions app named App1 that uses an HTTP trigger, runs on an Elastic Premium plan, and uses virtual network integration.
A partner application sends requests to App1 from a public IP address of xxx.xxx.xxx.xx.
You need to ensure that the requests are accepted from only xxx.xxx.xxx.xx.
What should you do?
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You have an Amazon Web Services (AWS) account connected to Defender for Cloud that has the Defender Cloud Security Posture Management (CSPM) plan enabled.
You need to identify the potential impact of security incidents that exploit multiple risks reported by Defender CSPM.
What should you use?
You have an Azure subscription.
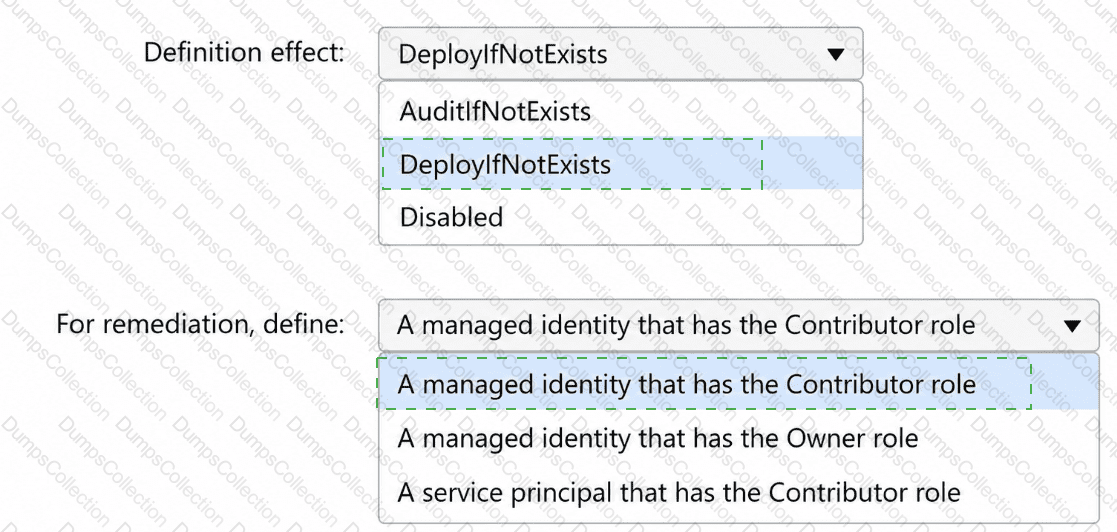
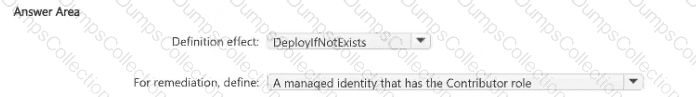
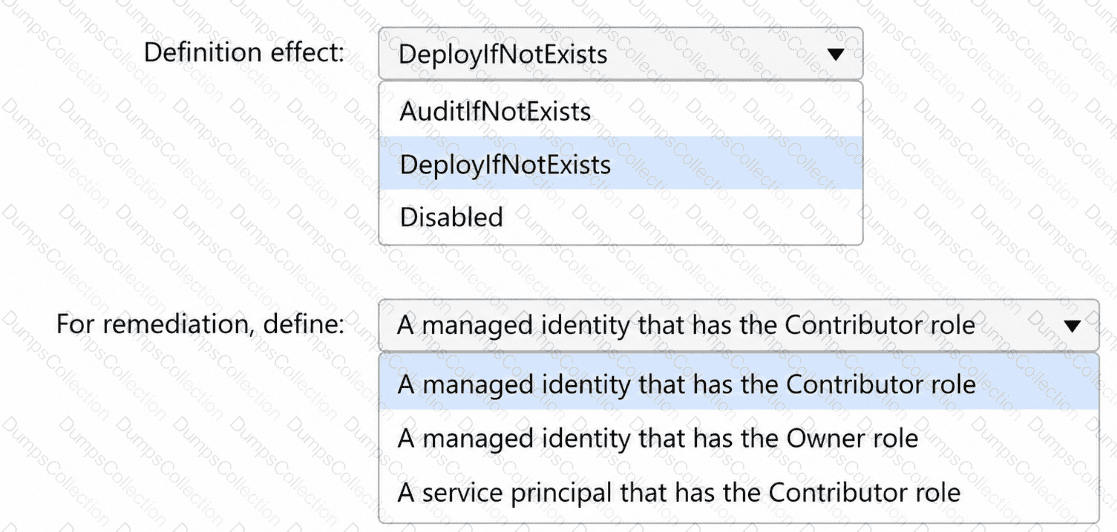
You need to create and deploy an Azure policy that meets the following requirements:
•When a new virtual machine is deployed, automatically install a custom security extension.
•Trigger an autogenerated remediation task for non-compliant virtual machines to install the extension.
What should you include in the policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have an Azure subscription named Sub1 that contains an Azure Kubernetes Service (AKS) cluster named cluster1 and an Azure container registry named ACR1 Sub1 has Microsoft Defender for Containers enabled, and runtime protection is active on cluster!
The developers at your company deploy pods that have elevated privileges, and the deployments are created in cluster1
You need to prevent pods with elevated privileges from being accepted by cluster!
What should you do?
TESTED 29 Sep 2026