Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: discbf75DC

Page: 1 / 2
Total 20 questions
Exam Code: JN0-336                Update: Oct 17, 2026
Exam Name: Security, Specialist (JNCIS-SEC)

Juniper Security, Specialist (JNCIS-SEC) JN0-336 Exam Dumps: Updated Questions & Answers (October 2026)

Question # 1

Regarding static attack object groups, which two statements are true? (Choose two.)

A.

Matching attack objects are automatically added to a custom group.

B.

Group membership automatically changes when Juniper updates the IPS signature database.

C.

Group membership does not automatically change when Juniper updates the IPS signature database.

D.

You must manually add matching attack objects to a custom group.

Question # 2

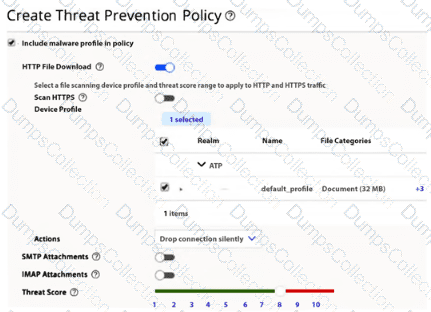
Referring to the exhibit, what should you do to ensure that Juniper ATP Cloud detects malware in HTTPS traffic?
A.

Manually configure and apply an SSL proxy profile.

B.

Lower the threat score.

C.

Configure a new device profile that includes encrypted traffic.

D.

Change the action to redirect the encrypted traffic to a decryption device.

Question # 3

Which two statements about proxy IDs are correct? (Choose two.)

A.

Proxy IDs cannot override default Junos behavior.

B.

By default, for a route-based IPsec VPN, a Junos security device sets the proxy ID to 0.0.0.0/0.

C.

Proxy IDs must match on both peers for a Phase 2 tunnel to establish.

D.

Proxy IDs are created during IKE Phase 1.

Question # 4

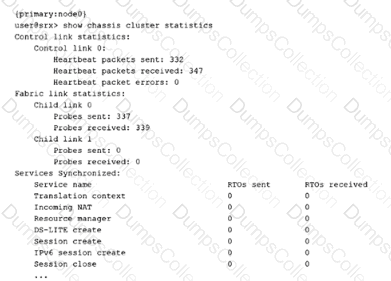
Referring to the exhibit, which two statements are correct? (Choose two.)
A.

Fabric link 0 is working.

B.

The control link is working.

C.

Fabric link 1 is failing.

D.

The control link is failing.

Question # 5

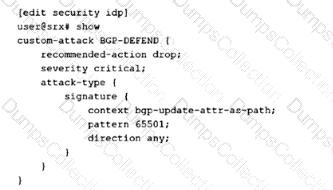
Which action will the SRX Series device take if traffic matches the custom attack object shown in the exhibit?
A.

the action taken is defined in the IDP policy that includes this attack object.

B.

the action taken is defined by the security policy.

C.

The SRX Series device will reject the traffic.

D.

The SRX series device will drop the traffic.

Question # 6

In Juniper high availability (HA) SRX Series device implementations, which interface will be used to exchange session state, configuration files, and ensure session continuity across nodes using the proprietary Trivial Network Protocol?

A.

fab

B.

fxp0

C.

fxp1

D.

swfab

Question # 7

Which three different objects would be created, modified, cloned, and deleted in the Shared Objects workspace of Junos Space Security Director? (Choose three.)

A.

geo IP

B.

IP address

C.

audit logs

D.

policy enforcement groups

E.

policy rules

Question # 8

What are two chassis cluster data plane interfaces? (Choose two.)

A.

swfab

B.

fab

C.

fxp1

D.

fxp0

Question # 9

Which two services would an SRX Series device use to connect to an LDAP server for identity-aware security policies? (Choose two.)

A.

Active Directory

B.

TACACS+

C.

RADIUS

D.

JIMS

Question # 10

Which two functions does Juniper ATP Cloud perform to reduce delays in the inspection of files? (Choose two.)
A.

Juniper ATP Cloud allows the creation of allowlists.

B.

Juniper ATP Cloud uses a single antivirus software package to analyze files.

C.

Juniper ATP Cloud allows end users to bypass the inspection of files.

D.

Juniper ATP Cloud performs a cache lookup on files.

Page: 1 / 2
Total 20 questions

Most Popular Certification Exams

Payment


Contact us

Site Secure

mcafee secure

TESTED 17 Oct 2026